
Copilot Studio governance: 6 checks before agents reach matter data
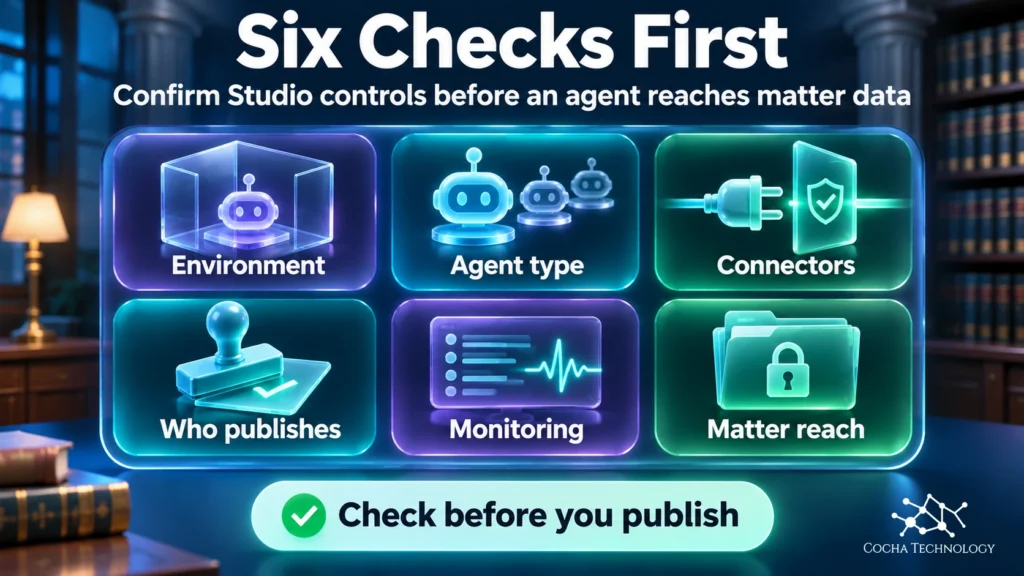
Copilot Studio governance for law firms comes down to six checks: environment, agent type, connectors, who publishes, monitoring, and matter data reach. Here is what Microsoft documents and where firm IT still has to decide.
Entra Agent ID: 6 Controls Before Law Firm Agents Go Live
Entra Agent ID gives each AI agent its own tenant identity. This guide walks law firm IT through six controls to set, from sponsors to Conditional Access, before agents can reach matter data.
Permission Creep Before You Turn On Copilot
Permission creep is the slow buildup of SharePoint access nobody decided to grant. Copilot makes that access easy to find. Here is what it is, where it hides in a law firm tenant, and six cleanup steps.
Harvey vs Legora: what IT should compare first
Harvey vs Legora is an IT comparison before it is a model-quality contest. Compare identity, retention, connector scopes, and cost levers while the pilot is still small, using only what each vendor documents.
Information Barriers and Copilot: what the wall covers
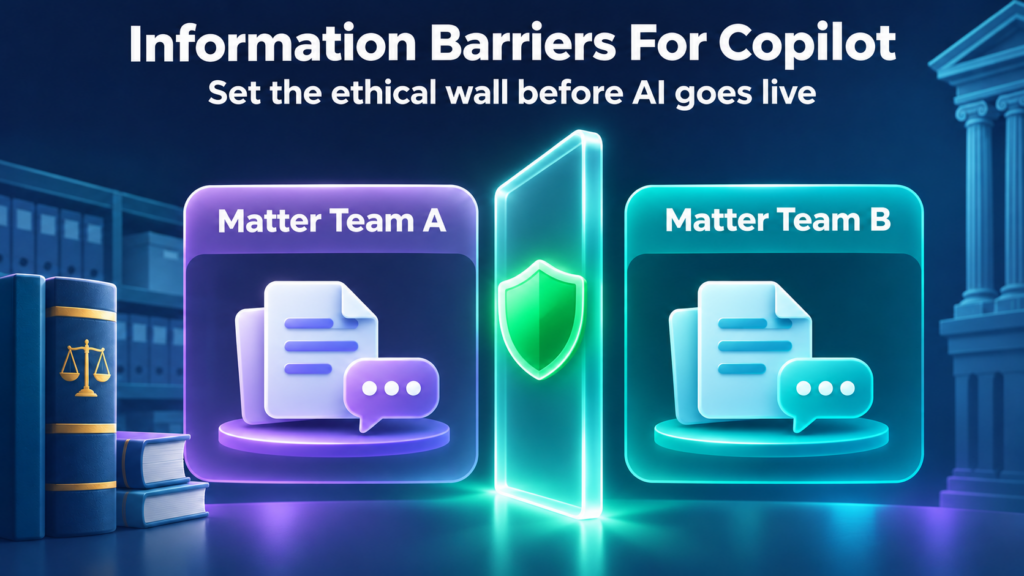
Information Barriers restrict Teams, SharePoint, and OneDrive collaboration. They do not restrict email. Copilot follows the user’s existing permissions, so test the wall in each workload before you assign seats.
AISPM vs DSPM: what to compare before you buy another posture tool
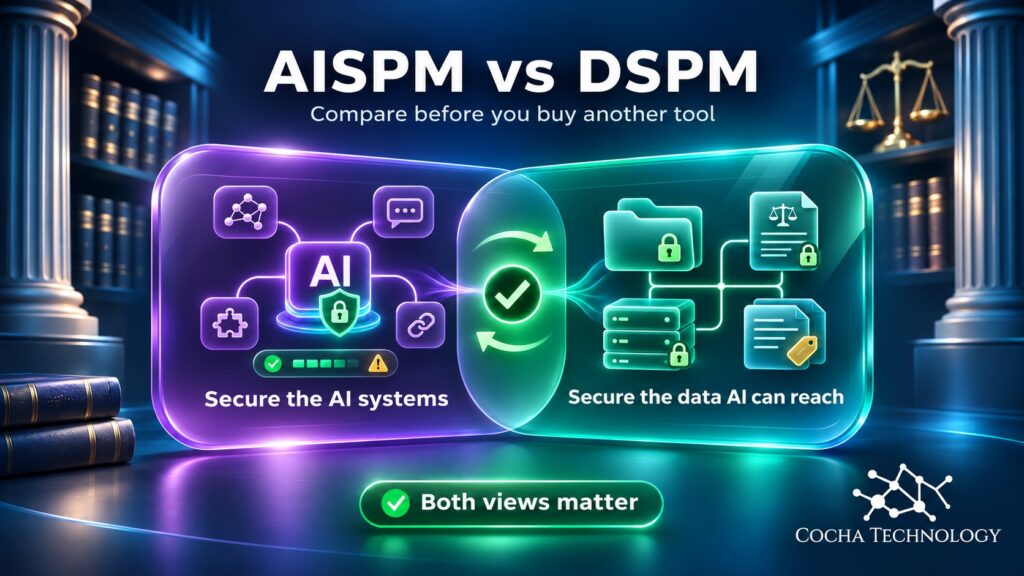
AISPM checks how AI systems are configured. DSPM checks what sensitive data those systems can reach. For law firm IT teams running Copilot or Claude pilots, we’d usually start with the data question.
MCP Gateway Security for Law Firms: Control AI Agent Access to SharePoint and iManage
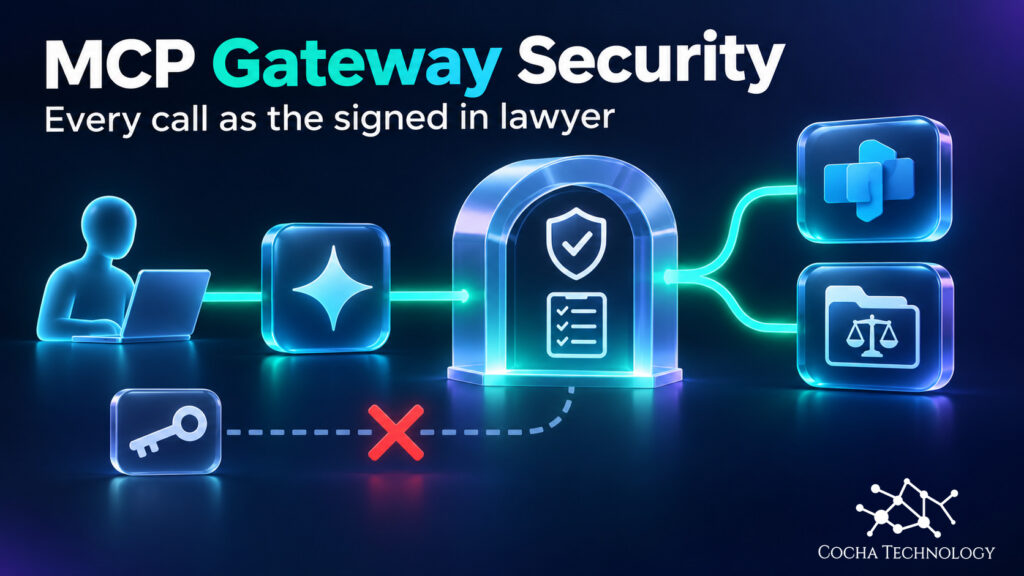
An MCP gateway only protects client documents if every call reaches SharePoint or iManage as the signed-in lawyer, with that lawyer’s own permissions. This guide covers the identity question, what the specification requires, a controls checklist and a test.
Gate AI connector expansion after a bounded AI pilot
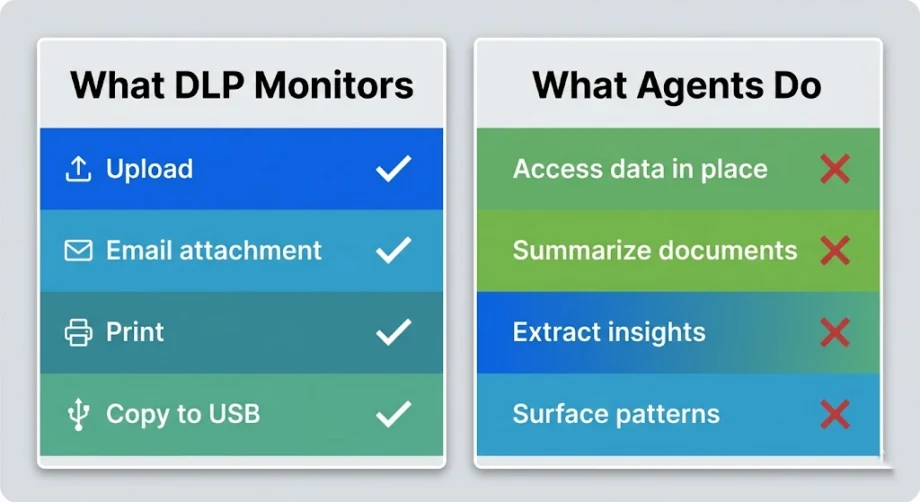
A completed pilot does not approve another connector. Use a separate go/no-go record to weigh access evidence, action scope, investigation readiness, and the conditions that would require reversing an expansion decision.
Approve a new AI workflow before you scale it
Policy permission does not approve a specific workflow. Build an AI workflow approval process that names the owners, attaches technical evidence, and records the changes that require another decision before expansion.
Make a law firm AI acceptable use policy enforceable
Enforcing an AI policy takes more than a launch announcement. Review monitoring evidence, track exceptions with expiry dates, and define how the firm responds when users bypass approved boundaries after launch.