Microsoft Copilot Governance: 5 Changes for Law Firms
If your firm rolled out Microsoft 365 Copilot sometime in the last year and hasn’t touched the governance settings since, July was the month that decision came back around. Microsoft pushed through three separate changes this month, new licensing prerequisites for Agent 365, an updated Partner Code of Conduct, and a watermarking policy for AI […]
Microsoft 365 Default Settings: 5 Critical Security Changes to Implement Right Now
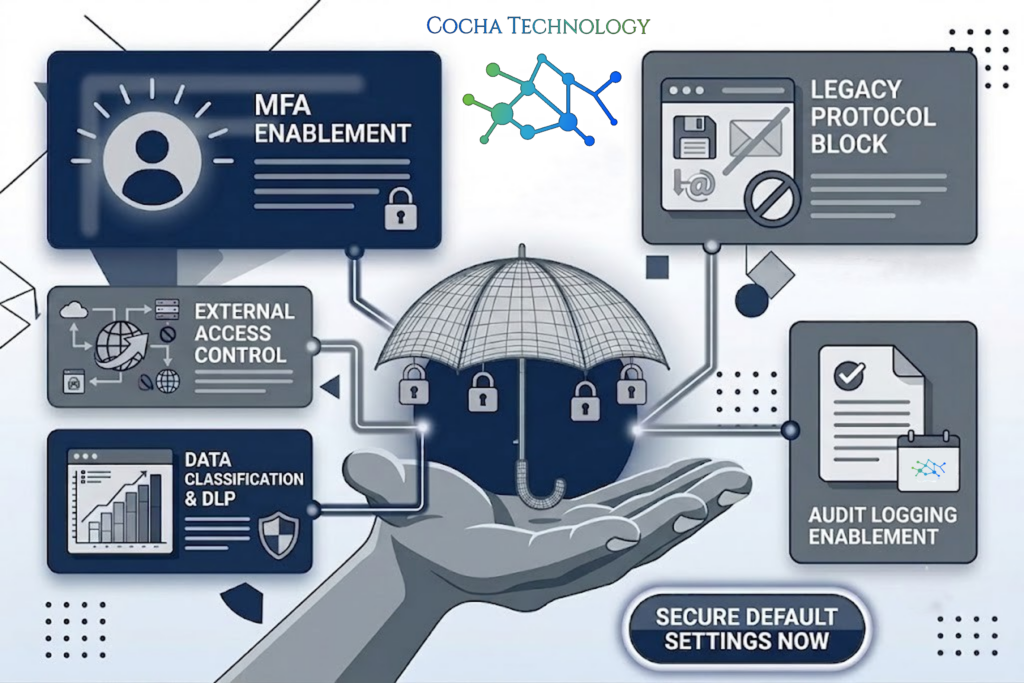
When navigating cloud business tools, there is a massive difference between an environment that is merely “functional” and one that is genuinely “defensible.” As we have unraveled throughout this series, relying on factory-default parameters is an active operational liability. Leaving your system unconfigured creates massive forensic blind spots, drains your technology budget through licensing inefficiencies, […]
Microsoft 365 Compliance Tools: 3 Heavy Risks Threatening Your Government Bids
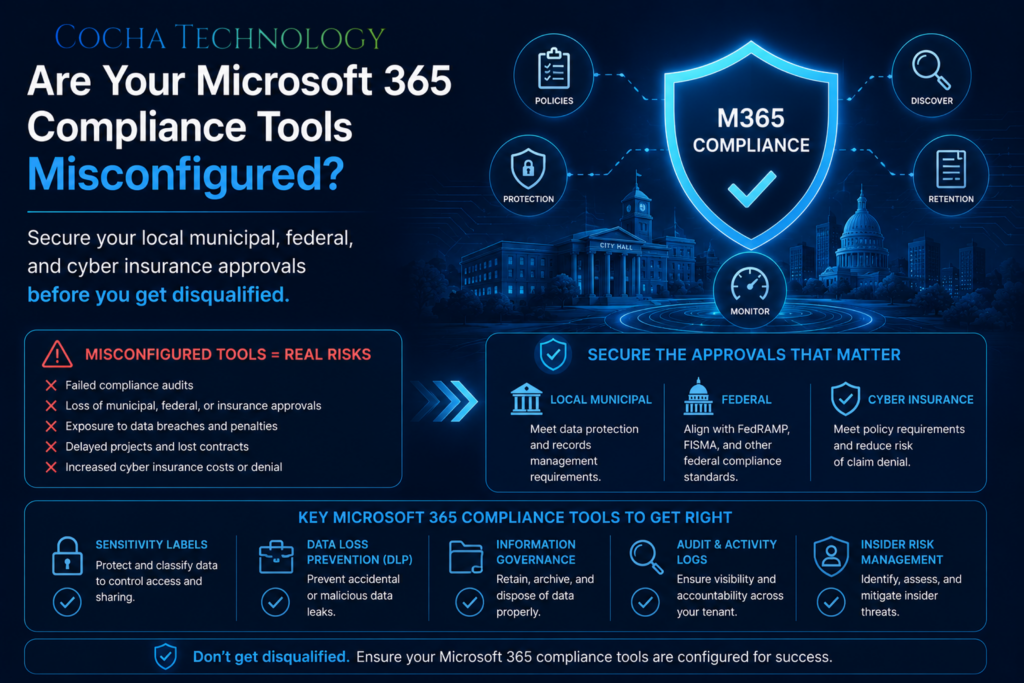
Mid-way through 2026, the evaluation metric for securing corporate partnerships and lucrative municipal contracts has fundamentally shifted. There was a time when filling out a request for proposal (RFP) meant showcasing your operational capacity, your past performance, and your competitive pricing structure. Today, you can deliver a flawless proposal, hold elite certification statuses, and still […]
Microsoft 365 Default Settings Danger: 1 Crucial Blind Spot Exposing Your Business
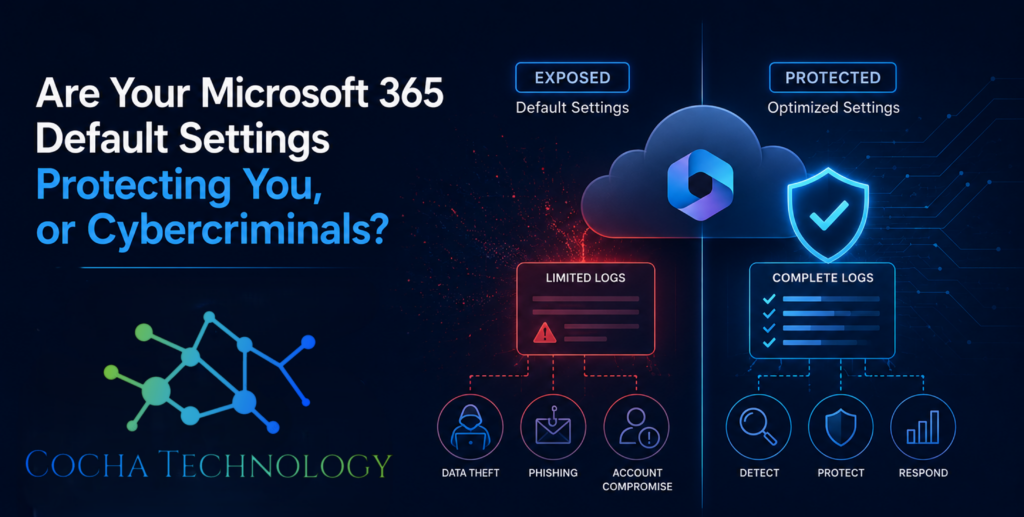
There is a distinct moment in our line of work that never gets easier to watch. It is the moment an entrepreneur looks at a screen, realizes their operations have ground to a halt, and asks, “But wait… aren’t we saving backups to the cloud? Doesn’t our subscription protect us from this?” It’s a fair […]
Misconfigured Storage in Azure: Why One Public Blob Puts Your Entire Tenant at Risk
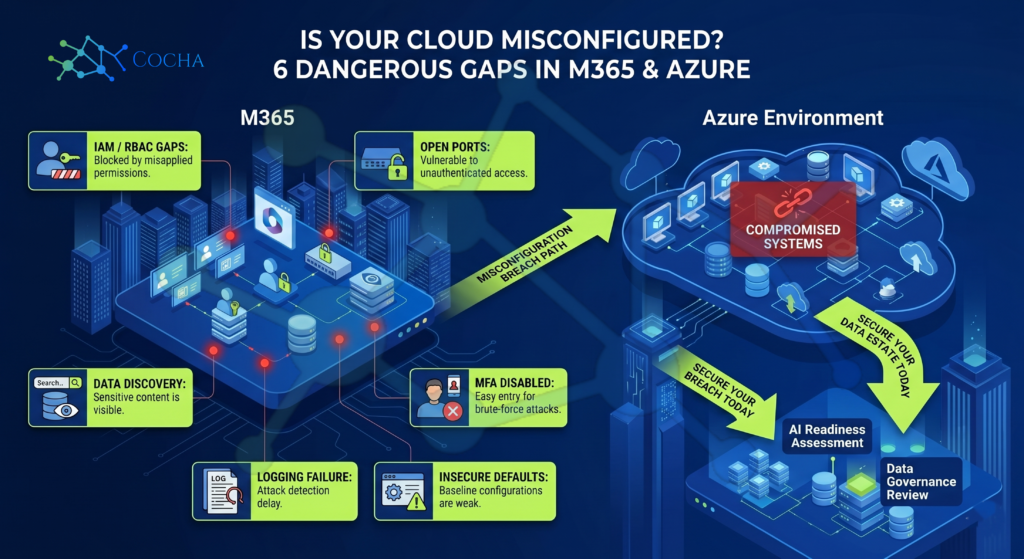
Back in late 2023, security researchers uncovered a massive data exposure incident that shook the tech world: a misconfigured storage bucket exposed a staggering 38 terabytes of private corporate information, including passwords, secret keys, and internal communication logs. The twist? The data belonged to Microsoft’s own internal AI research team. If the very engineers who […]
AI Readiness Assessment for Medical Device Manufacturers: Why FDA Audit Risk Starts in Your M365 Tenant
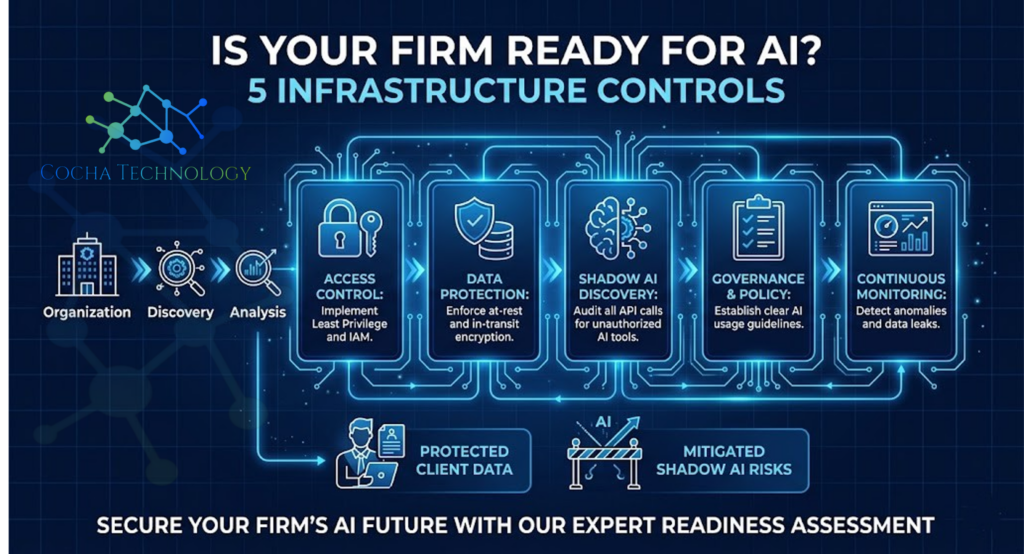
An FDA inspector will not walk into your facility and ask to review your theoretical corporate position on artificial intelligence. Instead, they will ask to see your data governance documentation, your electronic signature records, your access control logs, and your continuous audit trails. If your team has already deployed automated intelligence or cognitive agents without […]
Zero Trust Assessment: What It Actually Covers and Why Your Azure Migration Depends on It
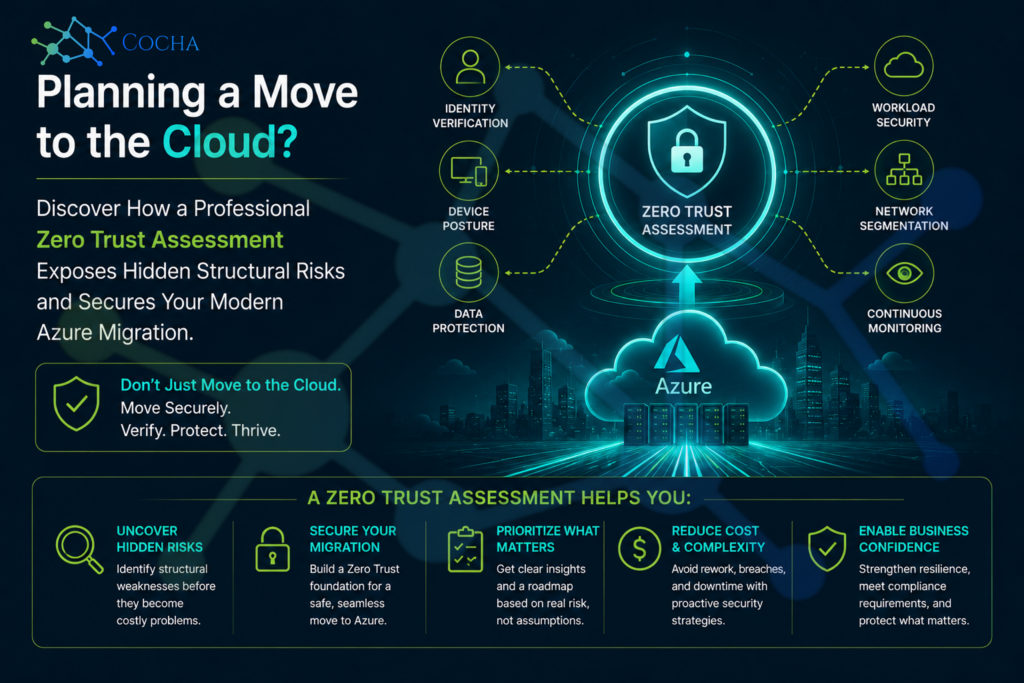
Depending on which tech vendor’s brochure you happen to be reading, Zero Trust is described alternately as a philosophical breakthrough, a singular software platform, or a mandatory compliance buzzword. If you are an IT director or a business leader tasked with maintaining an enterprise defense system, this marketing noise makes it incredibly difficult to understand […]
AI Readiness for Oil and Gas: Why ISO 27001 Alignment Is the Critical Baseline Before Any Agent Deployment
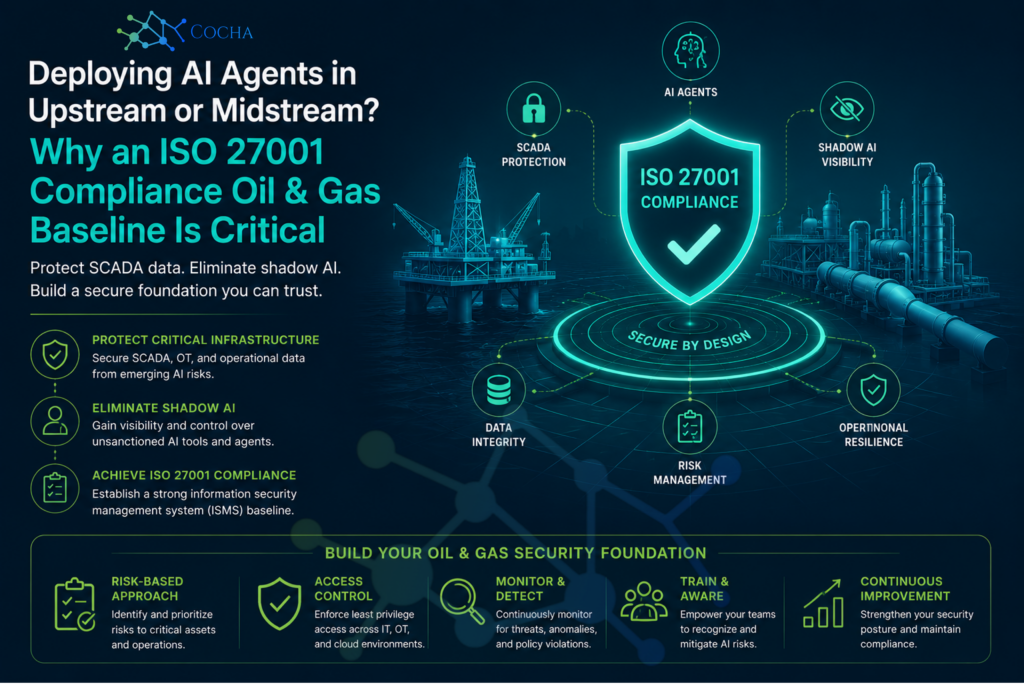
An independent midstream operator recently sat down with us to review an enterprise vendor security questionnaire. One specific question asked whether their IT infrastructure was aligned with ISO 27001 standards. The internal IT team confidently checked “Yes.” They had firewall policies, strong passwords, and a solid network perimeter. Technically, their answer met the basic criteria […]
What Is Cloud Misconfiguration? The 6 Most Dangerous Gaps in M365 and Azure Environments
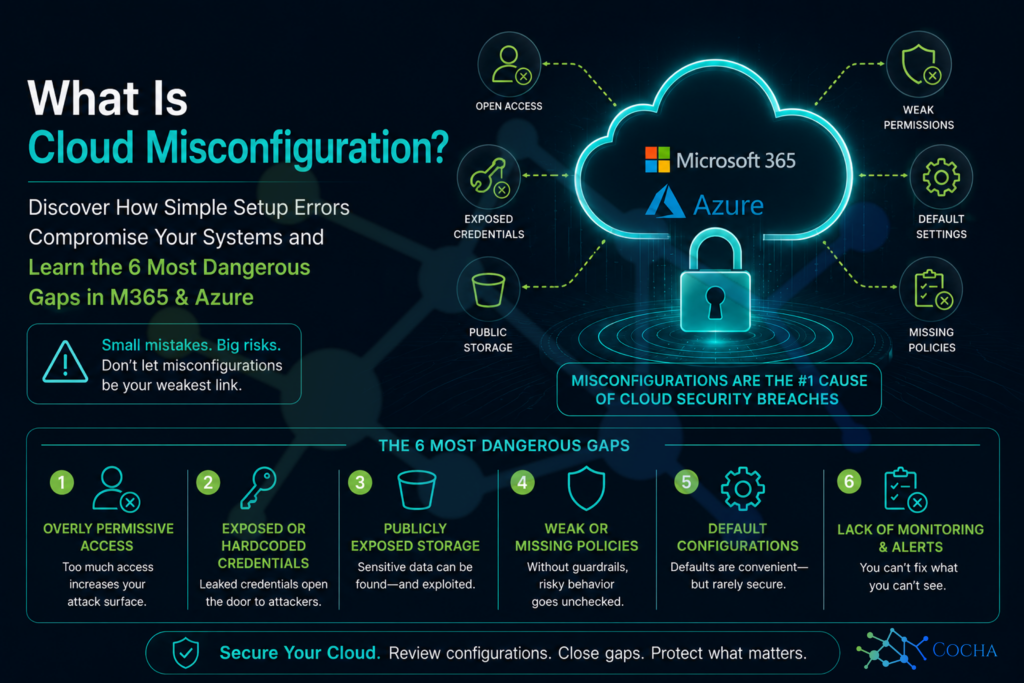
When most business owners and IT directors think about cyber threats, they picture highly sophisticated global syndicates writing complex code to crack into their networks. They imagine movie-style “zero-day” exploits that take weeks to engineer. But out here in the real world, the truth is far more ordinary. Most devastating data breaches don’t start with […]
AI Readiness Assessment Law Firm Guide: 5 Infrastructure Controls to Protect Client Data
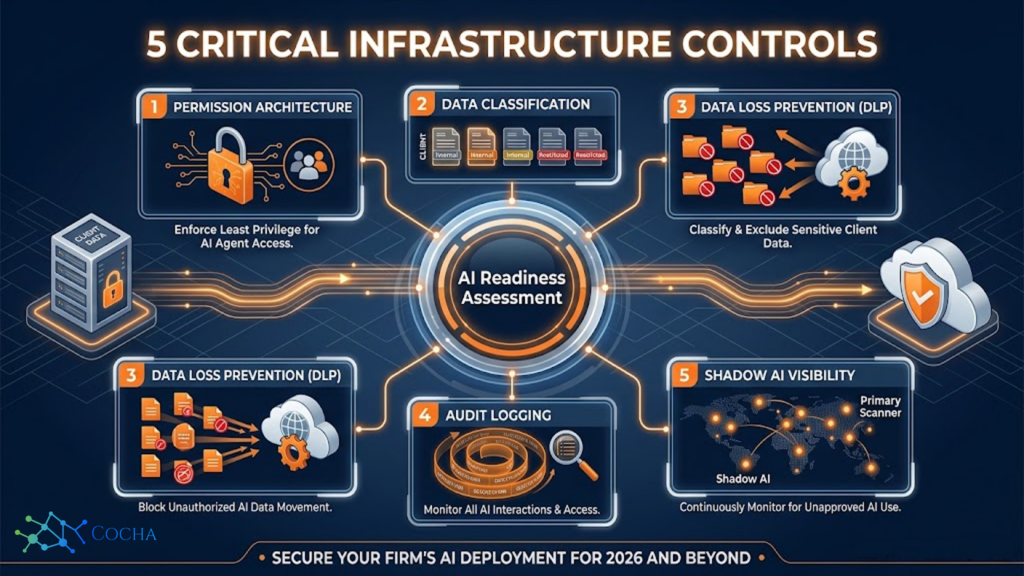
The managing partner of a mid-sized firm recently shared a story with me that should serve as a wake-up call for the entire legal industry. The firm had just approved Microsoft 365 Copilot. IT, eager to support the firm’s innovation goals, enabled the licenses and sent out a “Getting Started” PDF. Six weeks later, a […]