Copilot Studio: 6 controls before staff build their own agents

The free tier is already at your associates’ desks. Here are the admin controls to set now.
March 27, 2026
Copilot Chat Basic is the no-added-cost Copilot tier included with qualifying Microsoft 365 commercial subscriptions, so most of your associates already have it. It’s grounded in the web and doesn’t search your SharePoint unless someone pastes or uploads content. This guide covers the controls a law firm should set: access, web search, DLP, and logging.
The most important thing to understand upfront is this: Copilot Chat Basic is not a future consideration. Every user with a qualifying Microsoft 365 or Office 365 commercial subscription, meaning any account backed by a Microsoft Entra ID tenant, already has access to it. Whether or not your firm has officially launched an AI program, the tool is almost certainly already in use. The question is whether you are shaping that use or discovering it after the fact.
Before choosing an upgrade path, review which Microsoft 365 license includes what.
The single most persistent misconception among practice group leaders is that the free tier of Copilot is reading every file in the firm. It is not. Copilot Chat Basic is primarily web-grounded: it uses Bing to find publicly available information and a large language model to reason over it. It does not connect to your organization’s SharePoint, Exchange corpus, or any internal data repository unless a user explicitly provides content in the chat window. That connection to internal data is the exclusive territory of the paid M365 Copilot (Premium) tier via the Microsoft Graph.
When you’re ready, here’s when to move from Basic to Premium and what to lock down first.
The free tier has gone through several names as Microsoft has iterated on its product structure: it was originally called Copilot with Enterprise Data Protection (EDP), then simply Copilot Chat, and as of the April 15, 2026 rollout it is labeled Copilot Chat (Basic) in product interfaces. Understanding that naming history is useful when reading older vendor documentation.
While it does not index private data automatically, it can consume what a user actively provides. Firm data enters the chat in three ways:
Copilot data protection: what the EDP boundary means
Because these are commercial accounts with Entra ID, all Copilot Chat Basic interactions benefit from Enterprise Data Protection (EDP). Microsoft acts as a data processor under your organization’s Microsoft 365 commercial agreement. Prompts and uploaded data are not used to train the underlying public models. The data stays within the Microsoft 365 compliance boundary, subject to the same data residency, retention, and eDiscovery controls as the rest of your tenant. This is the same protection framework that governs your email and SharePoint data. See Microsoft Purview’s AI hub for the full compliance documentation.
Most firms do not want a firm-wide rollout before governance is in place. Copilot access control in Microsoft 365 operates at two levels: the tenant and the individual app. Here is how each works.
The primary lever for Copilot access control is the Copilot Control System inside the Microsoft 365 Admin Center. Go to:
From here, the “Copilot app” entry controls the web experience and the standalone desktop app. To restrict access to a specific group, such as a Technology Committee pilot, a particular practice group, or a subset of IT staff, go to:
Change the deployment status from “Everyone” to specific Azure AD security groups. Users outside those groups will not see the Copilot icon in the Microsoft 365 web portal or in the sidebars of their apps. This is the cleanest firm-wide access gate available without deploying endpoint policy. Deciding who gets Copilot is one control; deciding who can build and share agents inside it is another, covered in our Copilot Agent Builder controls guide.
Some firms want the standalone Copilot app available for general research but want to keep it out of Word or Excel, where a user might feed it a sensitive draft or a client document by mistake. Two mechanisms handle this:
Since Copilot relies on Connected Experiences to function within Office apps, disabling this setting for a specific app removes the Copilot sidebar from that app while leaving everything else intact. The user can still open the standalone Copilot app in a browser.
Post-April 15 note
After April 15, 2026, Copilot Chat Basic users will no longer have in-app sidebar access in Word, Excel, PowerPoint, or OneNote regardless of your Connected Experiences settings. The app-level suppression controls described above become primarily relevant for licensed M365 Copilot (Premium) users whose in-app integration you want to restrict on specific machines or for specific groups.
In Microsoft Teams, the presence of the Copilot app is governed by Teams App Setup Policies. The standard approach for a controlled rollout is:
This gives you a clean on/off switch per group without touching Intune or Cloud Policy.
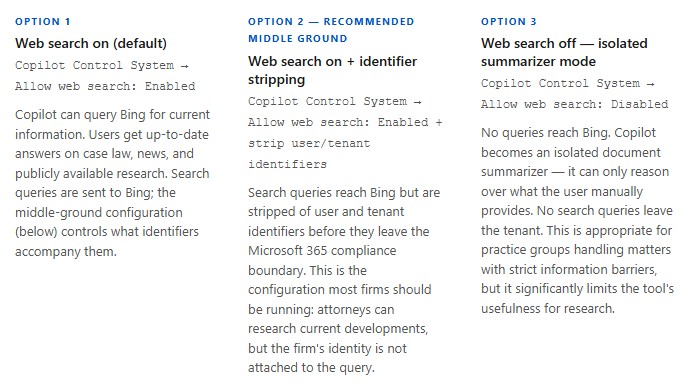
Because Copilot Chat Basic is grounded in the web, the Copilot web search policy is the single most impactful setting available to most firms. It controls whether the tool can query Bing at all, and what identifiers accompany those queries.
The setting lives in the Copilot Control System under the “Allow web search in Copilot“ policy. Here are the three configurations and their practical implications for a law firm:
Practical recommendation
For most law firms, the right Copilot web search policy is Option 2: web search enabled with identifier stripping. It preserves the research value of the tool while ensuring that Bing cannot correlate search behavior back to your firm or a specific attorney. If you have practice groups that require stricter isolation, such as international arbitration, M&A, or regulatory investigations, consider creating a separate Azure AD group for those users and applying Option 3 to that group specifically via a scoped policy.
File uploads are one of the riskiest features in Copilot Chat Basic. Any user can drag a PDF, a brief, or a contract into the chat. Plan around one limit: Microsoft Purview DLP can’t scan the contents of files uploaded directly into a prompt. It checks only the text typed into the prompt itself (Microsoft Learn).
Here’s what a DLP policy on the Microsoft 365 Copilot and Copilot Chat location can do, per the same Microsoft Learn page:
Microsoft’s licensing notes for these controls are linked from the same Learn page.
The audit infrastructure for Copilot is available today and most firms are not using it. Copilot Interaction logs are available through the standard Audit log search in the Microsoft Purview Compliance portal. Go to:
The logs show who is using the tool, which apps they are using it in, and whether they are uploading files. This data is the foundation for a fact-based conversation with practice group leaders about how AI is being used in their groups, rather than on assumptions in either direction.
The table below is designed to be shared with practice group leaders and your help desk team. It covers the post-April 15 state of Copilot Chat Basic across every Microsoft 365 surface a law firm attorney is likely to encounter.
| App / Surface | Copilot Chat Basic (no paid license) | M365 Copilot Premium (paid license) | Admin control |
|---|---|---|---|
| Word | ✗ Removed Apr 15 Sidebar access ends; users redirected to standalone app | ✓ Full integration Write, summarize, format in-document | Intune / Cloud Policy (Connected Experiences) |
| Excel | ✗ Removed Apr 15 | ✓ Full integration Formula help, data analysis | Intune / Cloud Policy |
| PowerPoint | ✗ Removed Apr 15 | ✓ Full integration | Intune / Cloud Policy |
| OneNote | ✗ Removed Apr 15 | ✓ Full integration | Intune / Cloud Policy |
| Outlook | ✓ Retained Email summarization & calendar grounding confirmed | ✓ Full integration | Copilot Control System |
| Teams | ○ Configurable App available; pinning controlled by admin | ✓ Full integration | Teams App Setup Policies |
| Standalone Copilot app (m365copilot.com) | ✓ Available Web + file upload; primary surface post-Apr 15 | ✓ Available | Integrated Apps (Admin Center) |
| Microsoft Edge sidebar | ○ Available Web-grounded; same EDP protections | ✓ Available | Edge management policies |
Not on its own. Copilot Chat Basic is grounded in the web and works with content a user pastes or uploads into the chat. It doesn’t search your SharePoint libraries the way licensed Microsoft 365 Copilot does. The risk is what people paste, so pair it with a policy and DLP.
Yes. In the Microsoft 365 admin center, Integrated Apps lets you change the Copilot deployment from everyone to specific security groups. In Teams, app setup policies control who has the Copilot app pinned. Start with a pilot group, then widen access once web search, DLP, and logging settings are in place.
The free version of Copilot should not be ignored simply because your firm has not purchased paid licenses. The tool is already in use. The governance question isn’t whether attorneys are using AI. It’s whether they’re using it within a managed boundary or outside one.
By taking control of the Copilot access control settings in Integrated Apps and configuring the right Copilot web search policy for each practice group, a firm can shape the AI habit before it becomes a shadow IT problem. A group-based rollout, a Copilot DLP policy that covers prompts and labeled content, and clear communication about the difference between web-grounded and work-grounded data are the best first steps.
Don’t let unmanaged AI become your next shadow IT headache. Talk with us about these controls, or start with the free AI Readiness Snapshot.
Call or email Cocha. We can help with your cybersecurity needs!