What an AI Readiness Assessment Covers After Your Snapshot
An AI readiness assessment covers a deeper, separately scoped review after your free Snapshot. It is not a free offer on this page.
A permission finding might be something your administrator can fix. A broader access problem may need investigation before anyone changes a policy. Your Snapshot findings help you decide where to start.
If you haven’t completed a Snapshot, start there. Cocha’s free AI Readiness Snapshot reviews your priorities and available evidence, then provides written findings for your team to work through.
Start with findings you can review
The Snapshot includes a working session of about 60 minutes, a client-run read-only SharePoint exposure script, and a live Microsoft Secure Score review. We discuss data security, access reviews, monitoring, Shadow AI, and your security baseline.
You receive written findings within five business days after the session and receipt of the required inputs, followed by a 30-minute walkthrough. Findings identify priorities and limitations. They don’t establish that every site or AI workflow has been checked.
No changes to your environment. No software to install. Your administrator reviews and runs the read-only script, then shares its output through an agreed secure method.
The Snapshot does not include a full DLP audit, a complete tenant permissions review, or a 90-day remediation plan. There is no obligation to purchase paid work.
Decide what your team can handle
Start with the evidence behind each finding. Confirm who owns the affected system and whether your team has enough information to make a change safely.
For a law firm, the question may be whether a matter workspace is available to people who no longer need access. An administrator may be able to resolve a specific permission issue. A pattern across workspaces needs a broader review.
Cocha is based in Houston. This guidance is written for law firms with 25 to 200 people, working with their internal IT team or MSP.
When findings need a deeper plan
After the Snapshot, we can discuss whether a paid AI Readiness Assessment would help answer unresolved questions. It is a separately agreed planning step, not a required follow-on to the free session.
Depending on the findings, that discussion may cover DLP behavior and data classification, wider SharePoint permissions, or on-premises file access. Connector and Graph API access scope may also need attention, along with Shadow AI evidence and mapping to relevant compliance frameworks.
A scoped Assessment takes two to four weeks and develops a prioritized 90-day remediation plan with effort estimates and a sequence for the agreed work. The 90 days describe the plan’s horizon, not a promise that all remediation will be complete.
Scope, evidence requirements, timing, and pricing are agreed before paid work begins. Implementation is separate.
Findings, planning, and implementation are different work
The Snapshot gives your team written findings and priorities. It does not change your environment.
Implementation comes later, if needed. A separately scoped Minimum Safe Sprint runs four to six weeks and focuses on a limited Copilot or Claude rollout. Typical work includes permissions cleanup and sensitivity labels where they block progress.
DLP moves from simulation to enforcement only with client approval. Conditional Access, guest access, and pilot boundaries are addressed as agreed. This is limited pilot work, not a firm-wide rollout or a managed security service.
Already completed your Snapshot?
Bring the questions your team couldn’t resolve during the findings review. We can discuss what needs more evidence and whether further planning makes sense before you commit to paid work.
Discuss your Snapshot findings
If you haven’t had a Snapshot, the free session is the starting point.
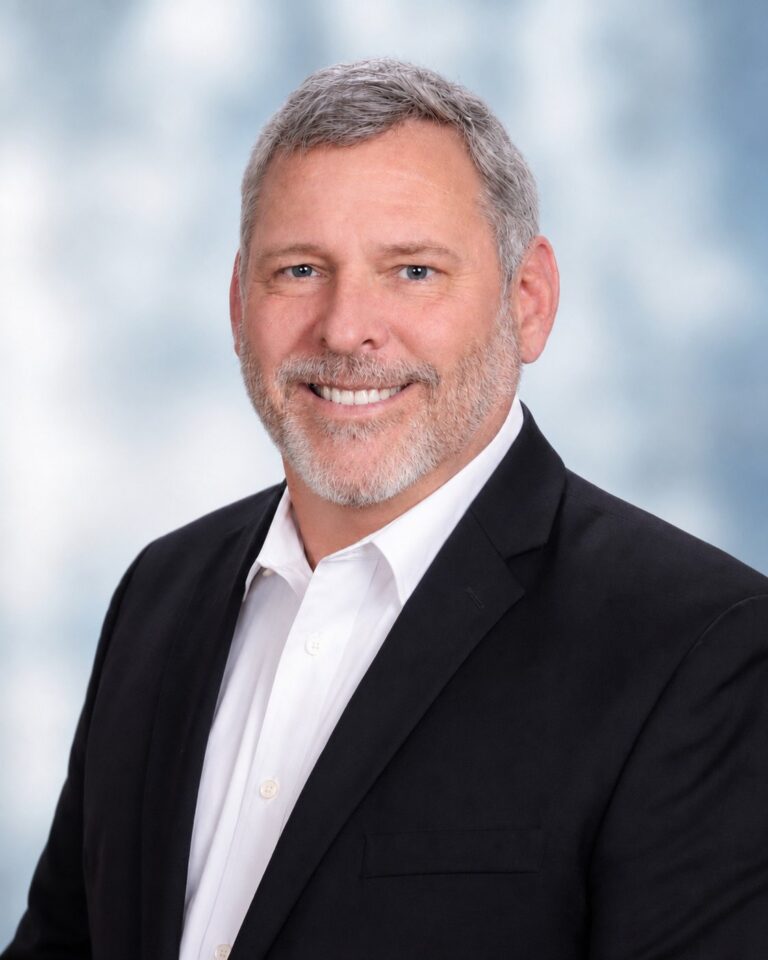
Steven R. Combs | Co-Founder and Principal, Cocha Technology
Steven is a fractional CIO/CISO with 30+ years of enterprise IT and security leadership. He has built AI governance frameworks for organizations with 1,700+ users, led enterprise Microsoft Copilot deployments, and conducted security assessments across law firms, energy companies, financial institutions, and PE-backed manufacturers. He holds certifications in Varonis, Check Point, FinOps, and Microsoft 365 security.